


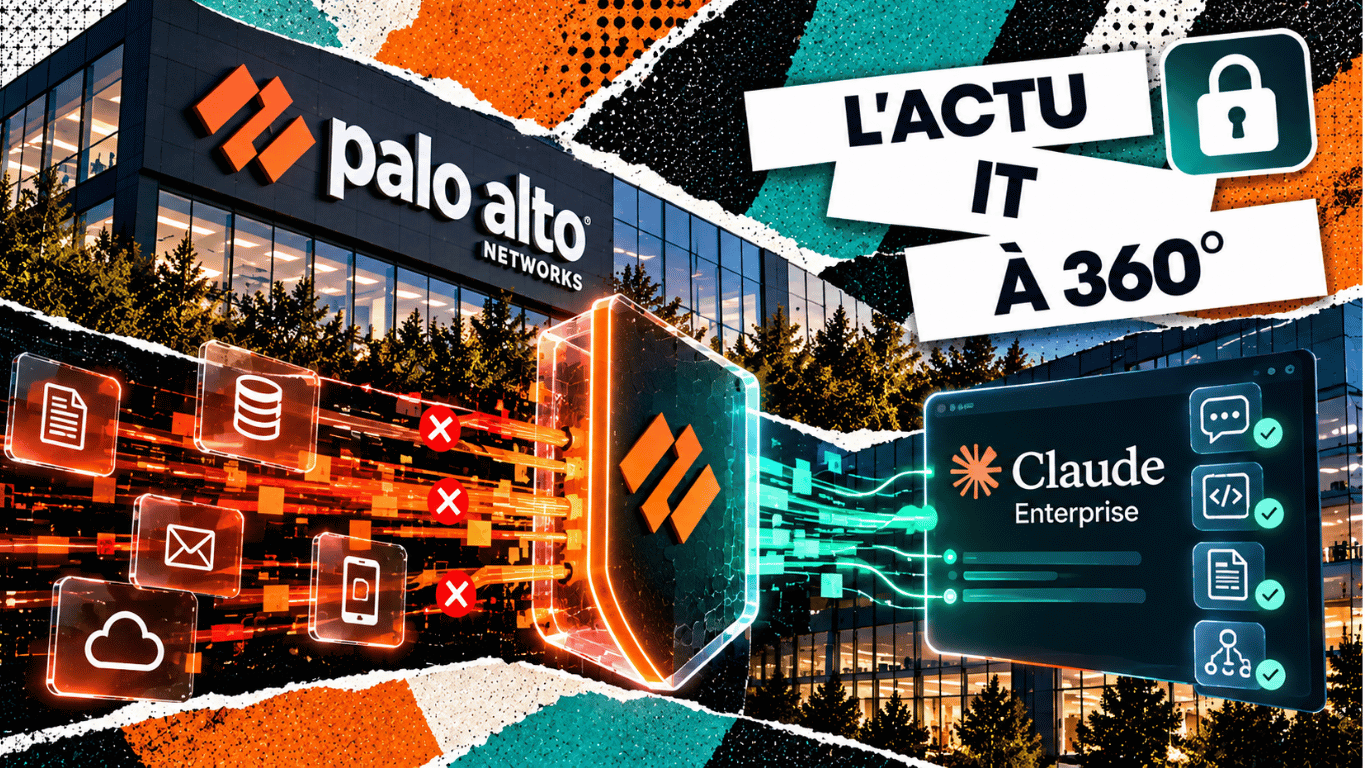
PPalo Alto Networks has unveiled several updates to Prisma AIRS: protection of interactions with Claude Enterprise, analysis of the components used by agents and control of their exchanges with tools.[1] The stakes are concrete for businesses: preventing an assistant from passing on confidential information or following a malicious instruction it encounters while working. These controls should support the use of AI without being mistaken for a guarantee of absolute security.
An integration with Claude already described in August
The 15 October announcement highlights a direct integration with Claude Enterprise covering Claude Code, Claude.ai and Claude Cowork.[1] However, this connection had already been presented in a vendor article dated 5 August 2026.[2] The October news should therefore be read as a set of security updates rather than the first appearance of this integration.
The mechanism relies on “inference hooks”, checkpoints before the model processes content. According to the description published in August, Claude sends the content to Prisma AIRS, which assesses it against the configured security profile and returns a decision to allow or block it.[2]
This architecture places the check before inference, that is, before the model runs on the request. It does not mean that the data stays on the employee’s device: the inspection flow is itself part of the scope to examine during integration.
Protecting data and spotting hijacked instructions
Palo Alto Networks says it reuses its data loss prevention (DLP) policies to control, among other things, personal information, proprietary code and sensitive credentials. The vendor also describes mechanisms for detecting prompt injections and attempts to bypass rules.[2]
A prompt injection seeks to pass off untrusted content as an instruction the assistant should follow. A document to be summarised might, for example, contain a directive telling it to ignore its task. The difficulty lies in distinguishing information that should be analysed from instructions that must never override the work requested.
Three points of control along the agent’s path
This editorial grid distinguishes between the announced functions and the checks useful for assessing them.
| Component | Operational effect | Control question |
|---|---|---|
| Components | Analyse models and skills before deployment.[1] | Which versions and dependencies have been examined? |
| Interactions with Claude | Allow or block content before inference.[2] | Which data triggers a block, and how can this be checked? |
| MCP exchanges | Inspect tool inputs and outputs.[1] | Do all relevant flows actually go through the control? |
The software supply chain now includes skills
The announcement extends AI software supply chain analysis to agent skills and introduces controls designed to identify malicious code before deployment.[1] A skill can bundle instructions, resources and code to help an agent carry out a task. Adding one therefore changes what the system can do and the components it relies on.
Reviews must remain tied to a specific version. Updates and any new access requested must be checked.
Tool calls are another point of control
Prisma AIRS AI Gateway is designed to inspect MCP exchanges in both directions, block certain hidden instructions, mask sensitive data in outputs and enforce access policies.[1] MCP is a protocol that allows AI applications to connect to tools and resources.
For SMEs, testing a development assistant on a limited scope
An SME using Claude Enterprise could start with a pilot project using dummy data. It would test whether a fake secret placed in the context is blocked, then how the system behaves when faced with an unwanted instruction in a document. This scenario is a suggested qualification approach, not a published customer result.
The assessment should measure the threats detected, the legitimate requests blocked and the delay added to exchanges. It should also specify what happens if the inspection service becomes unavailable. The announcements consulted provide neither an independent detection rate nor a detailed availability timetable for each feature.
Professionals fine-tune the rules and check their effect
This development calls directly on Cybersecurity skills. Professionals must identify the information to be protected, define the access required and translate company rules into verifiable controls. A policy that is too vague can let sensitive data through or needlessly hinder work.
Their role includes preparing tests and analysing alerts. A block does not in itself prove that an attack was prevented; nor does the absence of an alert show that an interaction was safe. Results must be reviewed with users and application owners.
New tools and skill updates can change the risks. Controls must be maintained, permissions reviewed and incident handling organised, with the ability to take back control.
Protection will depend on how much real usage is covered
The value of Prisma AIRS lies in bringing several controls closer to how tasks actually unfold. Their effectiveness will depend on the flows inspected, the rules configured and maintenance practices. Allowing an interaction guarantees neither the accuracy of the response nor the appropriateness of the action: business validation remains necessary.
Further reading
Four CCCLX reads on component security and the control of agents in the enterprise.
Azure Linux 4.0: is Microsoft preparing for life after Windows Server?
Open-source security scales up: IBM, Red Hat and Palo Alto join forces
GitHub Copilot bulks up for business: coding agents come under IT control
AI voice agents: Oracle details a LiveKit architecture on OCI
Sources
- 01
Gilmartin, J., Palo Alto Networks (15 October 2026). “Agentic Innovation Meets Enterprise Control”. Overview of Prisma AIRS updates for interactions with Claude, the AI software supply chain and exchanges with tools.
- 02
Thellmann, S. and Hanumanula, S., Palo Alto Networks (5 August 2026). “Prisma AIRS: Unified Data Protection for Claude”. Description of the Prisma AIRS integration with Claude Enterprise and the pre-inference controls.
Djinn Stealer: the malware targeting companies’ cloud and AI credentials
Cybercriminals are changing targets Cyberattacks are no longer aimed solely at data or workstations. The credentials used to access cloud platforms, artificial intelligence environments and development tools have become highly sought-after assets. It is against this...
Claude Tag turns Slack into a genuine agentic workspace
AI agents settle at the heart of collaborative work Artificial intelligence is no longer limited to assistants accessed in a chat window. With Claude Tag, Anthropic is taking a new step by building an AI agent directly into Slack. Available in beta for Claude...
IBM and OpenAI want to arm businesses against machine-speed cyberattacks
Defenders must now fight AI with AI Cyberattacks are evolving at unprecedented speed. Thanks to artificial intelligence models, attackers can automate the search for vulnerabilities, analyse code in seconds and quickly identify the most exposed systems. To respond to...
Open-source security scales up: IBM, Red Hat and Palo Alto join forces
Cyberattacks push IT giants to join forces Open-source components are present in virtually all modern applications, from cloud platforms to business software. This dependence, however, comes with a growing risk: vulnerabilities are now discovered and exploited much...
With Lambda, AWS prepares cloud infrastructure for autonomous AI agents
Serverless enters a new phase The cloud is evolving to meet the needs of a new generation of applications based on agentic artificial intelligence. As AI agents become capable of carrying out complex tasks for hours at a time, traditional serverless architectures are...
With Code Layers, Figma brings design and development together for good
A new step towards building apps without boundaries Design and software development have long followed two separate paths. Designers imagined the interfaces, developers then translated them into code, with many back-and-forth exchanges and sometimes discrepancies...
Google Chrome sees what you see: Gemini can now analyse your screen
Chrome takes a new step towards the intelligent browser Web browsers no longer simply display web pages. They are gradually becoming genuine assistants capable of understanding the context in which users are working. With the new “Select from screen” feature, Google...
SpaceX buys Cursor: agentic AI becomes the new standard in software development
An acquisition that reaches far beyond the software world SpaceX’s acquisition of Anysphere, the company behind Cursor, for an estimated $60 billion marks a major turning point in the tech industry. Behind this spectacular deal lies a much deeper transformation: the...
Europe’s AI takes shape: OVHcloud is developing its own LLMs
OVHcloud wants to move from cloud to artificial intelligence Long recognised as a major player in European cloud, OVHcloud now aims to play a much bigger role in the artificial intelligence ecosystem. At the VivaTech trade show, Octave Klaba, the group’s founder and...
F5 strengthens its WAF to tackle the cyber threats of the AI era
Cyberattacks are evolving faster than patches Artificial intelligence is transforming corporate cybersecurity, but it is also benefiting attackers. New models capable of rapidly identifying vulnerabilities or automating certain exploitation phases are dramatically...