


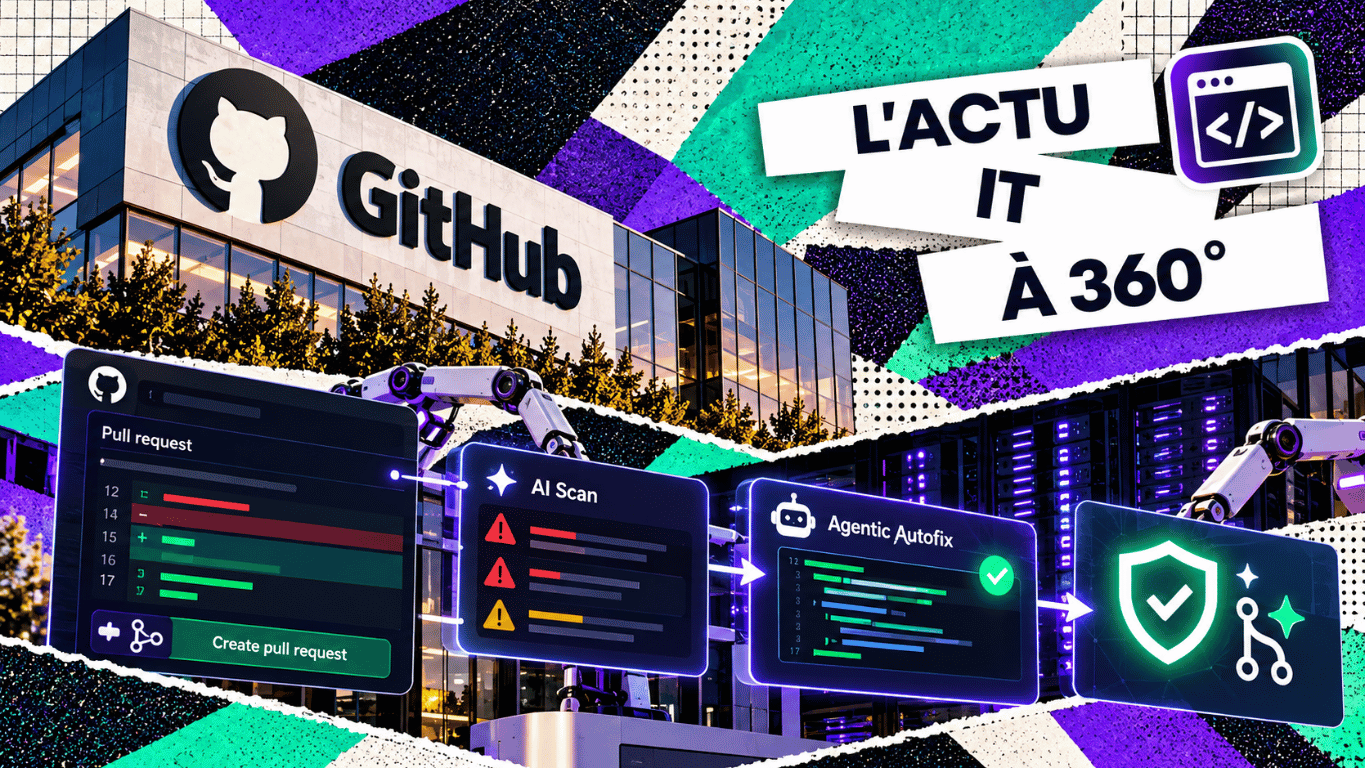
GitHub has announced the general availability of AI Scan for pull requests and Agentic Autofix for code scanning alerts.[1][2] These features bring AI assistance closer to the work of securing code. They do, however, operate on different scopes: proposed changes for the former, alerts on the default branch for the latter. For businesses, the challenge is to prepare fixes more effectively while keeping technical validation in place before they are merged.
AI Scan reviews changes before they are merged
A pull request is used to propose a change and have it reviewed before it is merged. AI Scan complements CodeQL there, notably for PHP, Bash, Terraform and certain less well-covered frameworks. Once enabled alongside code scanning, it surfaces findings flagged as AI-generated, sometimes accompanied by an explanation and a suggested fix.[1]
These findings remain advisory: they do not cause the code scanning check to fail and do not block merging via ruleset requirements. AI Scan does not process pull requests from forks or those created by Dependabot.[1] A team must therefore organise how these findings are read and dealt with, without assuming that their presence automatically holds up a release.
Agentic Autofix prepares a fix from an existing alert
Agentic Autofix can be assigned a code scanning alert located on the default branch. It explores the relevant files, proposes a change, re-runs CodeQL and can iterate before opening a draft pull request for review.[2]
GitHub explicitly excludes alerts that exist only in a pull request or another branch from this assignment to Copilot.[2] The two new features should therefore not be described as an automatic pipeline in which every AI Scan finding is immediately handed over to Agentic Autofix.
An alert disappearing on a new scan gives a useful indication about the targeted issue. It does not prove that the application retains all its expected behaviour, nor that the change introduces no other defect. Functional tests and a review of the change remain necessary.
Two paths and a human decision
The table distinguishes between the announced features and the responsibility of the team using them.
| Stage | What GitHub provides | Team check |
|---|---|---|
| Detection during review | AI Scan flags risks in proposed changes.[1] | Assess the risk and decide how to handle it before merging. |
| Preparing the fix | Agentic Autofix works on an alert from the default branch.[2] | Review the modified files and the relevance of the fix. |
| Validation | A new CodeQL scan accompanies the agent’s work.[2] | Also check business tests and side effects. |
Access conditions matter when choosing a pilot
AI Scan is available for public repositories; private or internal organisation repositories require GitHub Code Security or GitHub Advanced Security. A Copilot licence is not required.[1] Agentic Autofix is aimed at customers of these offerings on GitHub Enterprise Cloud, with administrative activation and a defined Copilot billing method.[2]
Both features consume Code Security AI credits; Agentic Autofix also uses GitHub Actions minutes.[1][2] Before rolling out, SMEs need to check their plan, the scope of repositories and the associated budget. The economic benefit will depend as much on review time as on the number of fixes actually accepted.
SMEs can evaluate results in two distinct situations
First illustrative scenario: a team modifies a PHP form and receives a finding in its pull request. The developer checks whether user input can actually reach the sensitive operation, examines the suggestion, then adds a test reproducing the case. A plausible answer from the AI is not enough to establish whether the risk exists or has gone away.
Second scenario: a code scanning alert already exists on the default branch of an eligible repository. The team assigns it to Agentic Autofix, then reviews the proposal. It checks that the fix does not inadvertently change access rights, accepted formats or business results. These scenarios are an evaluation approach, not published customer results.
The pilot can track the time to a validated fix, the proportion of suggestions retained and the regressions detected. Counting only closed alerts could mask an excessive verification workload or unsuitable changes.
Developers must understand the vulnerability as well as the fix
This development raises the bar for Web Programming and Management. Reading code remains essential to understand the path data takes, spot a fragile assumption and determine whether the fix addresses the root cause. Professionals must be able to explain why a change reduces the risk.
The skill is also reflected in the quality of tests. A case that fails before the fix and passes afterwards provides a useful benchmark, to be complemented by checks on legitimate uses. In particular, a stricter control must not prevent a necessary function from working or shift the vulnerability elsewhere.
Finally, the developer organises the review and documents decisions. They must know when to accept a suggestion, modify it or reject it. Delegating to an agent can speed up preparatory work, but command of the application remains essential to decide what gets merged.
Editor’s note
The progress to measure is a fix that is understood, tested and maintainable. These tools can help reduce research and preparation work; their real value will depend on the coverage of the scans and on teams’ ability to verify the proposals.
Further reading
Four CCCLX reads on assisted development and software security.
Sandbox, terminal, policies: GitHub puts guardrails on its code agents
Project Glasswing: Anthropic goes on the offensive against software vulnerabilities
Open-source security changes scale: IBM, Red Hat and Palo Alto join forces
With Code Layers, Figma brings design and development firmly together
Sources
- 01
GitHub Changelog (15 October 2026). “AI Scan for pull requests generally available”. Overview of the general availability, scope and terms of use of AI Scan.
- 02
GitHub Changelog (15 October 2026). “Agentic autofix for code scanning alerts general availability”. Details of how Agentic Autofix works, its access conditions and billing.
PDFs, presentations, audio: Adobe wants to turn Acrobat into a content factory
Acrobat no longer just wants to open your documents For more than thirty years, Acrobat has mainly been used to read, create, edit, sign and share PDFs. Adobe now wants to give it a much broader role. On 9 September 2026, the company announced new capabilities based...
Salesforce plugs Claude into its CRM: Claudeforce prepares for life after the interface
What if the CRM soon no longer needed to be opened? For decades, using a CRM meant navigating between customer records, dashboards, menus and forms. With Claudeforce, Salesforce and Anthropic want to change this logic: rather than forcing users to go into Salesforce...
Kimi K3, Mistral, DeepSeek: Oracle turns OCI into an AI model hub
Oracle wants to make OCI a one-stop shop for AI Oracle is stepping up its efforts in the AI cloud battle by significantly expanding the catalogue of models available in OCI Enterprise AI. On 4 September 2026, the group announced in particular the integration of Kimi...
Agentic Data Cloud: Google rethinks data for the age of AI agents
AI agents are forcing Google to rethink data architecture AI agents promise to search for information, make decisions and act directly within company systems, but this autonomy depends on one essential condition: accessing the right data and, above all, understanding...
Google Cloud tackles the hidden bill of AI agents
AI agents raise a new problem: how much does a task really cost? As companies move from chatbots to AI agents able to work through multiple steps, the question of cost becomes much more complex. A chatbot generally handles a request and generates an answer, whereas an...
Workday, Navan, Avalara: ChatGPT Work moves into business software
ChatGPT Work is gradually leaving the chat window With GPT-6 Astra, OpenAI is no longer simply trying to improve the quality of ChatGPT’s answers. The company wants to bring its AI closer to the applications in which employees actually work. With the arrival of GPT-6...
From chip to cloud: Groq raises 350 million to scale up
Groq now wants to sell cloud rather than just chips Groq is pursuing a major strategic transformation. Long seen as one of Nvidia’s challengers thanks to its LPUs (Language Processing Units) specialised in artificial intelligence model inference, the group is now...
Muse Code: Meta launches its AI agent to tackle giant codebases
Meta wants to bring AI agents into complex software projects Meta is stepping up its efforts in AI-assisted software development with Muse Code, a new agent designed to work on large codebases, where traditional assistants can quickly lose the context needed to...
Qwen3.8-Max reportedly coded for 16 days without human intervention
Alibaba tests how far an autonomous AI developer can go Alibaba claims to have reached a new milestone in agentic software development with Qwen3.8-Max, its new flagship model launched in early August 2026. In an internal test, the model reportedly worked fully...
Two months, $1.1 billion: River AI is already exciting investors
A spectacular raise for a start-up barely out of the shadows Two months after emerging from stealth mode, River AI has just completed one of the most spectacular funding rounds of the year in artificial intelligence. The start-up founded by Igor Babuschkin, a former...